Custom Website Security Audit
A thorough security audit of your custom website — vulnerabilities, misconfigurations, malware, SSL and access risks, with a fix roadmap.
Explore MoreProtect your WordPress website by identifying potential vulnerabilities, unsafe configurations, and outdated components. ZyvenTech reviews your website's security setup to help you understand potential risks and take practical steps to address them.
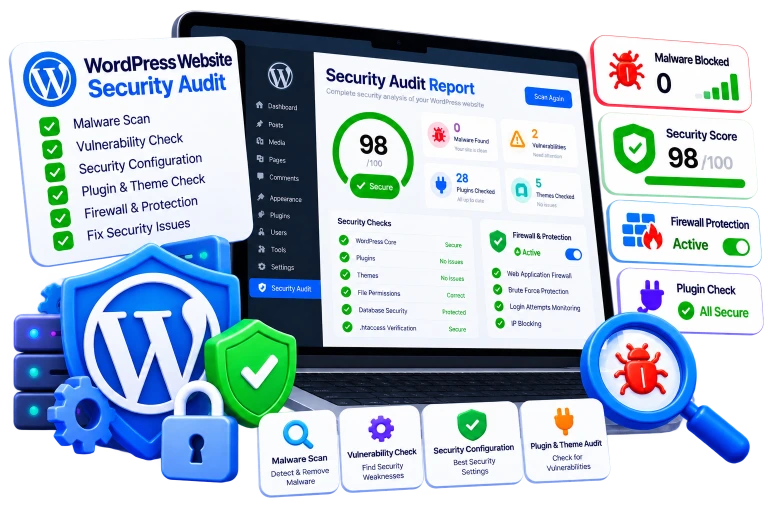
The majority of hacked WordPress sites share the same story: an outdated plugin, a weak admin account, or hardening steps nobody took. A WordPress-specific audit looks precisely where WordPress sites actually break.
We review your core, theme and plugins, user accounts, hosting configuration and security settings, check for malware and signs of compromise, and deliver a prioritized hardening roadmap.
Comprehensive evaluation of your WordPress environment, plugins, database, authentication, and hosting configuration.
Check your WordPress installation for outdated versions, known security concerns, and configuration issues that may require attention.
Review installed themes and plugins for outdated versions, known vulnerabilities, unnecessary components, and potential compatibility concerns.
Assess login protection, administrator accounts, password practices, user roles, and permissions to identify potential access risks.
Inspect for indicators of malware, suspicious files, unexpected code changes, and other signs that may suggest a compromised website.
Review relevant WordPress settings, file permissions, debug settings, and other configuration options that may affect security.
Assess relevant database access controls, file permissions, exposed files, and configuration practices within the agreed audit scope.
Review HTTPS implementation and relevant security headers to identify configuration gaps that could affect website protection.
Review your backup arrangements, backup frequency, storage practices, and recovery procedures to help prepare for unexpected incidents.
A methodical 8-step assessment process to identify vulnerabilities, assess risks, and fortify your WordPress installation.
We review your WordPress website, hosting environment, business requirements, and audit objectives. Testing permissions and boundaries are confirmed before assessment.
We check the WordPress version, update status, relevant security notices, and configuration settings that may need attention.
We review active and inactive themes and plugins, check available updates, and identify known vulnerability concerns where information is available.
We assess administrator accounts, user roles, authentication settings, and relevant access controls to identify unnecessary privileges or weaknesses.
We inspect for suspicious code indicators and review relevant file permissions, configuration settings, and exposed resources.
We assess relevant hosting security settings, HTTPS configuration, backup practices, and recovery readiness within the agreed scope.
We document validated findings where practical, explain their potential impact, and prioritize recommended actions by severity and business risk.
We deliver a clear report with practical remediation guidance. Follow-up validation can be included if agreed as part of the service.
Key vectors, scanner databases, and configuration layers we inspect during your WordPress security assessment.
*Audits encompass both standard WordPress repositories and custom-coded child themes or third-party premium plugins.
WordPress provides a flexible website platform, but its security also depends on the components, configuration, hosting, and access controls surrounding it.
*An audit helps reduce risk, but it cannot guarantee that a website is completely secure or immune to future attacks.
The exact deliverables depend on your website, access permissions, audit depth, and selected package.
It is a structured review of your WordPress installation, themes, plugins, user permissions, configuration, and other relevant security controls to identify potential weaknesses.
Yes. We can review supported premium and free themes, their update status, configuration, and available vulnerability information.
Yes. The audit can include installed plugins, available updates, and known vulnerability information where reliable data is available.
We can check for common indicators of malware and suspicious changes using appropriate methods. However, no single scan can detect every form of compromise.
We aim to minimize disruption. Potentially disruptive tests require explicit approval and suitable safeguards. Some checks may be performed in a staging environment where practical.
The audit includes findings and remediation recommendations. Fixes, cleanup, updates, or hardening can be arranged separately or included in the agreed scope.
The timeline depends on the website's size, installed components, hosting environment, access arrangements, and depth of assessment.
We can discuss an assessment to investigate indicators of compromise. Malware cleanup, recovery, and incident response may require a separate scope.
A thorough security audit of your custom website — vulnerabilities, misconfigurations, malware, SSL and access risks, with a fix roadmap.
Explore MoreProfessional WordPress websites with modern UI, responsive development, SEO-friendly structure and speed optimization.
Explore MoreCustom-coded websites built around your business goals — fast, responsive, secure and designed to convert visitors into enquiries.
Explore MoreIdentify potential security weaknesses before they become bigger problems. ZyvenTech helps you assess your WordPress website, understand the risks, and plan practical improvements to protect your website and its data. Let's discuss your website and choose the right audit scope.